


 Claim Ownership
Cybersecurity Tech Brief By HackerNoon
Subscribed: 30Played: 166
Subscribe

© 2026 HackerNoon
Description
Learn the latest Cybersecurity updates in the tech world.
533 Episodes
Reverse

This story was originally published on HackerNoon at: https://hackernoon.com/does-the-internet-love-us-spoiler-no.
The internet was supposed to bring us closer. So how did we end up questioning what’s real, who’s human, and whether we can trust it at all?
From the ILOVEYOU virus to AI-powered cyberattacks and a web increasingly populated by machines, this is the story of our most complicated love affair, and why learning to let go might be our next great challenge.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #artificial-intelligence, #digital-culture, #future-of-internet, #social-media, #deepfakes, #internet, #history-of-the-internet, and more.
This story was written by: @francescocapria. Learn more about this writer by checking @francescocapria's about page,
and for more stories, please visit hackernoon.com.
The internet started as a knowledge-sharing project, became an all-consuming passion, and is now breaking up with us in four stages: Gen Z pulling back from social media, AI deepfakes destroying trust in what is real, AI-powered attacks turning love into hate, and a possible endgame where no one can tell human from machine — leaving acceptance, and rediscovering boredom, as the only way out.
This story was originally published on HackerNoon at: https://hackernoon.com/nosana-and-decentralized-compute-auditing-my-ai-security-platform-and-planning-the-gpu-experiment.
I audited my own AI security platform on Nosana and found a simulated GPU. Here is the plan.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #infosec, #fastapi, #ueba, #gpu-cloud, #decentralize-ai, #open-source, #decentralize-ai-hackathon, #nosana, and more.
This story was written by: @drechi. Learn more about this writer by checking @drechi's about page,
and for more stories, please visit hackernoon.com.
What it is: SentinelIQ is an open source FastAPI security pipeline covering behavior risk scoring, event correlation, MITRE ATT&CK T1110 mapping and simulated response. It is live on Nosana.
This story was originally published on HackerNoon at: https://hackernoon.com/stop-trusting-the-oauth-email-how-one-missing-check-enables-account-takeover-in-2026.
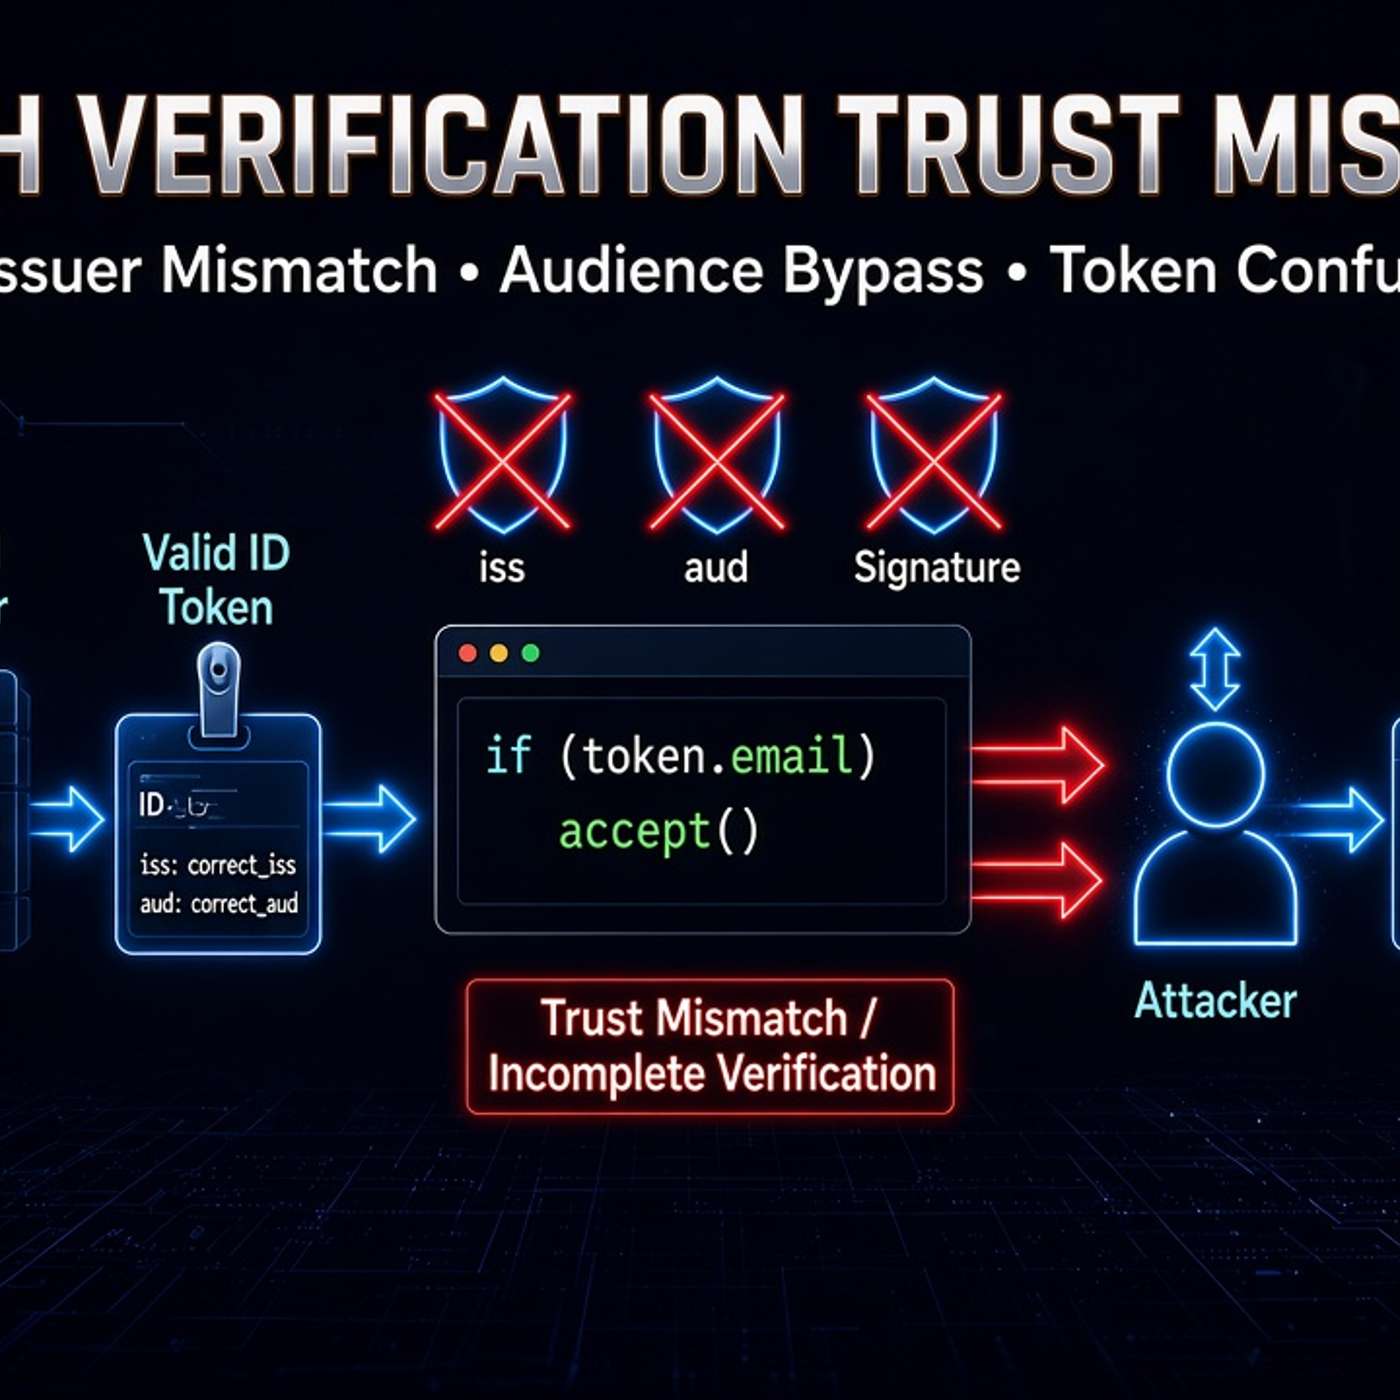
Explore OAuth Verification Trust Mismatch, a security issue caused by mismatch between OAuth providers and client applications
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #oauth-authentication, #web-security, #oauth-vulnerabilities, #hackernoon-top-story, #account-takeover, #vulnerabilities, and more.
This story was written by: @viodex. Learn more about this writer by checking @viodex's about page,
and for more stories, please visit hackernoon.com.
OAuth Verification Trust Mismatch vulnerabilities can arise when a client application incorrectly assumes an email address is verified based on an OAuth provider's authentication response, potentially leading to account takeover, blind linking, and other security issues.
This story was originally published on HackerNoon at: https://hackernoon.com/gcore-makes-enterprise-security-bundle-free-for-public-agencies-until-end-of-the-year.
The offer follows the php2shell vulnerabilities that forced public websites offline across Europe earlier this week.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #gcore, #cybernewswire, #press-release, #gcore-announcement, #cyber-threats, #cybercrime, #good-company, and more.
This story was written by: @cybernewswire. Learn more about this writer by checking @cybernewswire's about page,
and for more stories, please visit hackernoon.com.
Gcore is offering its WAAP Enterprise plan free of charge to government bodies and public agencies until December 31, 2026, to help them recover from the php2shell vulnerabilities. The plan blocks the attack path and allows sites to be brought back online while patching continues, providing a filtering layer that blocks the attack pattern.
This story was originally published on HackerNoon at: https://hackernoon.com/implementing-the-owasp-api-security-top-10-in-nodejs-and-postgresql.
OWASP API Security Top 10 (2023) with vulnerable code, working fixes and tests in Node.js: BOLA, auth, rate limits, SSRF and a CI authorization matrix.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #owasp, #api-security, #owasp-api-security-top-10, #express.js-security, #node.js-api-security, #api-authentication, #postgresql-row-level-security, #api-rate-limiting, and more.
This story was written by: @AJAYKUMAR_evq18mss. Learn more about this writer by checking @AJAYKUMAR_evq18mss's about page,
and for more stories, please visit hackernoon.com.
A hands-on walkthrough of the OWASP API Security Top 10 using a sample Node.js, Express, and PostgreSQL application. Each vulnerability is demonstrated through insecure code, followed by defensive implementations and automated tests. The guide covers authorization, authentication, resource limits, SSRF, configuration, and third-party API security, culminating in a CI authorization matrix.

Comments

Download from Google Play

Download from App Store
 United States